
Estimated reading time: 3 minutes
Table of contents
tl;dr: Color Profile Injection is due to untrusted inputs within color profile blobs.
Updated 13-AUG-2026: From the WASM Draft Security Model just Published: When the ICC Tools are compiled to WASM then integrated into a browser, attacker-controlled profile metadata or generated outputs may be rendered in the DOM. If the application inserts this data into HTML without proper output encoding, control sequences or crafted payloads can lead to DOM-based XSS, reflected XSS, or UI spoofing.
Why? Color profiles rely on offset and length fields, enabling crafted profile data to corrupt neighboring structures.

Color Profile Injection Background
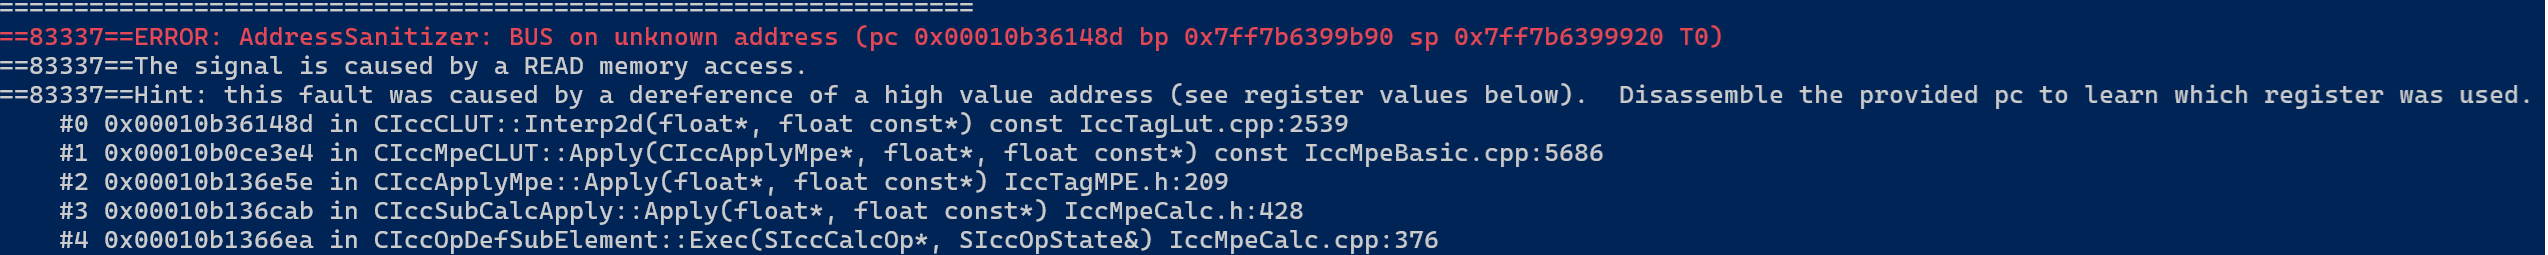
Color Profile Injection (CPI) occurs because user-controllable inputs can corrupt a color profile binary layout. Resulting impact includes memory corruption, logic bypasses, and potential code execution.
Cube ANSI Injection
iccFromCube can preserve or emit attacker-controlled ANSI escape sequences from a .cube file into generated ICC profile metadata, and related tooling such as iccDumpProfile / iccApplyToLink may render those sequences in terminal output. This can cause terminal injection, misleading output, and potential user interface spoofing when untrusted input is processed.
TITLE "iccDEV Maintainers"# cube file created by iccApplyToLink version 2.3.2.1+219f0bf## Profiles applied (by profile description):# - POCLUT_3D_SIZE 20.000000 0.000000 0.000000-12.885228 0.319194 1.386239-39.729450 1.775265 -5.271579-52.614677 1.792050 1.2630662.243681 -25.043680 0.3675932.089121 -23.969965 1.4173731.703325 1.296922 -3.8338761.467083 1.322401 1.298224
XXD
00000050: 20 50 72 6f 66 69 6c 65 73 20 61 70 70 6c 69 65 Profiles applie00000060: 64 20 28 62 79 20 70 72 6f 66 69 6c 65 20 64 65 d (by profile de00000070: 73 63 72 69 70 74 69 6f 6e 29 3a 0a 23 20 2d 20 scription):.# -00000080: 1b 5b 33 31 6d 50 4f 43 1b 5b 30 6d 0a 0a 4c 55 .[31mPOC.[0m..LU00000180: 0a
In Your Terminal

Profile Injection Defense in Depth
- Do not construct color profiles using string or byte concatenation.
- Check all user-controlled data that influences color profile content:
- Check & enforce fixed lengths
- Reject unexpected or unexpected binary data
- Make sure user input can’t affect offsets, tag counts, or size fields
Ineffective or Insufficient Input Sanitization
These controls are commonly used but are not sufficient:
- Escaping or limiting text input
Color profiles are binary formats; character-based sanitization does not prevent binary structure changes. - Trusting earlier data (second-order injection)
Color profile data that passes validation at creation time later be reprocessed. Different components can have different parsing assumptions. - Only using third-party libraries is not enough.
Libraries do not prevent injection when user input is allowed to influence structural fields such as offsets or lengths.
CWE References
- CWE-20 – Improper Input Validation
https://cwe.mitre.org/data/definitions/20.html - CWE-119 – Improper Restriction of Operations within the Bounds of a Memory Buffer
https://cwe.mitre.org/data/definitions/119.html - CWE-707 – Improper Neutralization
https://cwe.mitre.org/data/definitions/707.html
Knowledgebase
- https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-26730
- https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2023-32443
- https://bugs.chromium.org/p/project-zero/issues/detail?id=2226
- https://nvd.nist.gov/vuln/detail/CVE-2022-26730
- https://nvd.nist.gov/vuln/detail/CVE-2023-32443
You must be logged in to post a comment.